T1136.001 Create a new user in a command prompt
sub-technique for Local Account creation under the Persistence tactic
- ATT&CK technique
- T1136.001
- Tactic
- Persistence
- Status
- complete
Description
| Rule ID | Description | Level | Source | Event ID |
|---|---|---|---|---|
| 92036 | net.exe binary started by cmd shell | 3 | Sysmon | 1 |
| 92040 | net1.exe executed user creation command | 12 | Sysmon | 1 |
| 60160 | Domain Users Group changed | 5 | Security | 4728 |
| 60109 | User account created | 8 | Security | 4720 |
| 60109 | User account enabled | 8 | Security | 4722 |
| 60110 | User account changed | 8 | Security | 4738 |
| 60170 | Users Group changed | 5 | Security | 4732 |
JSON Excerpt of level 12 event
{
    "agent": {
      "ip": "192.168.56.20",
      "name": "WS01",
      "id": "001"
    },
    "data": {
      "win": {
        "eventdata": {
          "originalFileName": "net1.exe",
          "image": "C:\\\\Windows\\\\System32\\\\net1.exe",
          "description": "Net Command",
          "processId": "2808",
          "currentDirectory": "C:\\\\Users\\\\nehan.adm\\\\AppData\\\\Local\\\\Temp\\\\",
          "utcTime": "2026-10-14 04:36:35.677",
          "ruleName": "technique_id=T1136.001,technique_name=Local Account",
          "commandLine": "C:\\\\WINDOWS\\\\system32\\\\net1  user /add \\\"T1136.001_CMD\\\" \\\<redacted>\\\"",
          "user": "LAB\\\\nehan.adm",
          "parentUser": "LAB\\\\nehan.adm"
        },
        "system": {
          "eventID": "1",
          "channel": "Microsoft-Windows-Sysmon/Operational",
          "computer": "WS01.lab.local"
        }
      }
    },
    "rule": {
      "firedtimes": 1,
      "level": 12,
      "description": "net1.exe executed a user creation command",
      "groups": [
        "sysmon",
        "sysmon_eid1_detections",
        "windows"
      ],
      "mitre": {
        "technique": [
          "Local Account"
        ],
        "id": [
          "T1136.001"
        ],
        "tactic": [
          "Persistence"
        ]
      }
    }
}
Triage
The account name is not expected, “T1136.001_CMD”.
Created through net1.exe in TEMP.
LAB/nehan.adm ran the command, possible compromise of nehan.adm credentials.
Account has not logged in yet. No logon events present.
Was not added to a privleged group. (Only in local Users)
Conclusion: Moderate urgency, unusual behaviour.
Containment
Disable-LocalUser -Name "T1136.001_CMD"
Only disabling for forensic review.
Dealing with admin account
Running query session produced no evidence of active sessions.
Reset nehan.adm password immediately Set-ADAccountPassword -Identity "nehan.adm" -Reset -NewPassword (ConvertTo-SecureString "NewSecureLabAdmin!#2026" -AsPlainText -Force
Force immediate invalidation of Kerberos ticket’s by disabling and re-enabling the account:
Disable-ADAccount -Identity "nehan.adm"Enable-ADAccount -Identity "nehan.adm"
Test results and telemetry
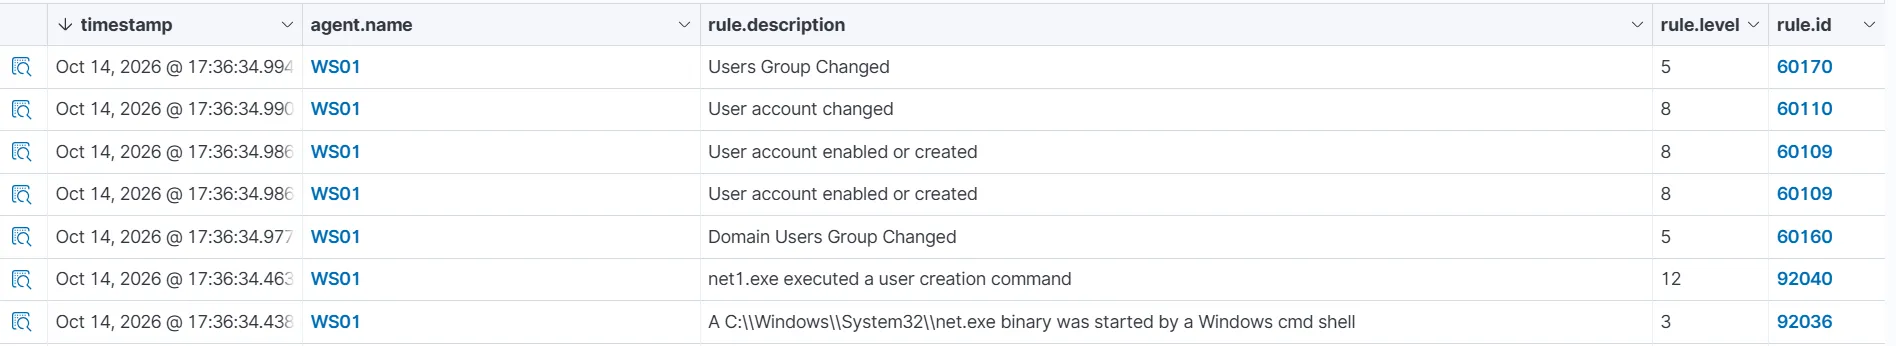 Figure 1: Dashboard alerts from T1136.001 Atomic